Every alert has a

Backstory is Stairwell's agentic investigator. It turns a single alert into a finished case: the full blast radius, the attack written out stage by stage, and specific remediation steps for every asset affected.

Prologue

An investigation usually runs across a sandbox, a threat intel lookup, an EDR search, and a ticket. Backstory runs it in one place, against every file you have collected.

Chapters

The investigation is only half the job. The other half is explaining it. Backstory writes the case stage by stage, in plain language, so the report is done before anyone asks for it.

Epilogue

No case ends in doubt. You know how far the attack reached and what to do about it, on every asset it touched.

Cover to cover on every alert

Complete investigations, run for you

Watch the story take shape

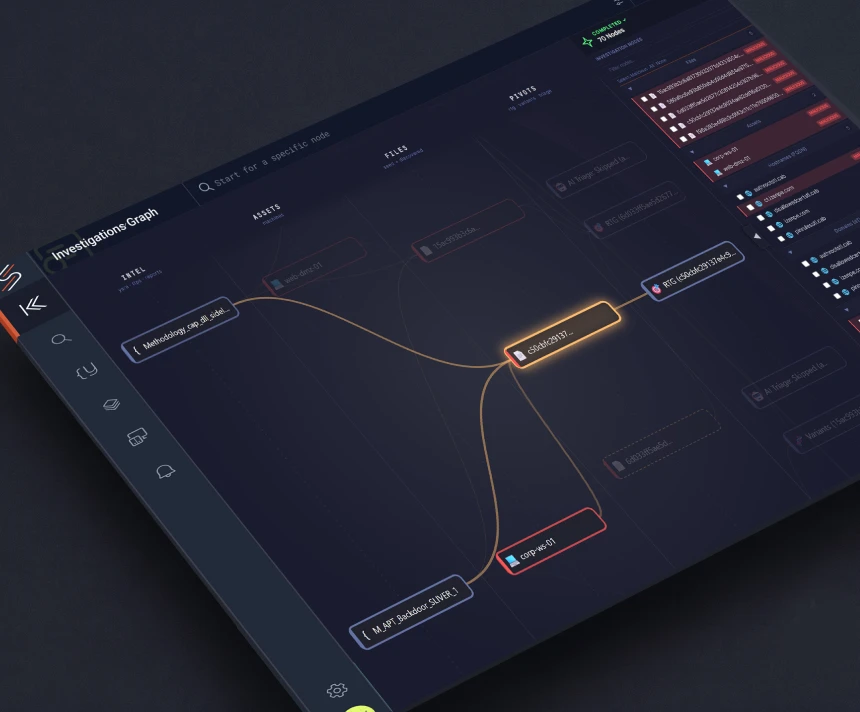
Every file, host, and domain connected to the alert, on one interactive map. Stay at the summary level, or click into any node and dig until you hit the detail you need.

Read the attack chapter by chapter

Stage by stage. What happened first, what it hit, what came next, with the what, where and when attached to each stage for full context.

Find the plot behind the TTP

The alert names a MITRE technique and stops there. Backstory tells you what that technique did on your machines, which files carried it, and how each one led to the next.

Finish the book

Close the case with actions. What to block, what to isolate, what to remove, and in which tool. Ready to hand to your EDR, your SIEM or your SOAR.

Send it back for a rewrite

Disagree with a verdict? Mark the asset clean or infected, regenerate the report, and the case is rebuilt around your judgment.

Backstory has a backstory

The intelligence foundation under every investigation

A PRIVATE REPOSITORY
FOR LIFE

Your files, preserved in a private repository and continuously compared against Stairwell’s
petabyte-scale corpus. 

PETABYTES

OF MALWARE

DETECTION

AT SCALE

790,000+ YARA rules 
run against every file. Private defenses attackers cannot see, test, or 
tune around.

1TB of YARA

SCANNED IN SECONDS

RECURSIVE VARIANT DISCOVERY

Start with one malicious file. Stairwell searches the full corpus to surface every related variant.

2.4 X


VARIANT DETECTION

THREAT

INTELLIGENCE

New threat reports 
become automatic hunts across every file in your environment, the moment they are published.

20+


THREAT SOURCES