EVIDENCE IN. ACTION OUT.

CONNECT THE INVESTIGATION TO THE TOOLS YOU ALREADY USE.

Bring alerts and suspicious files into Stairwell. Return Backstory verdicts, related variants, affected hosts, Rehunt matches, and remediation guidance to the tools your team already uses.
Stairwell works with the existing security stack, so analysts can investigate from preserved file evidence without creating another disconnected workflow.

How integrations work

Bring the evidence 

in

Collect the file behind an EDR alert, ingest campaign intelligence, or submit an artifact directly. Stairwell preserves it in your dedicated environment.

Investigate 

the alert

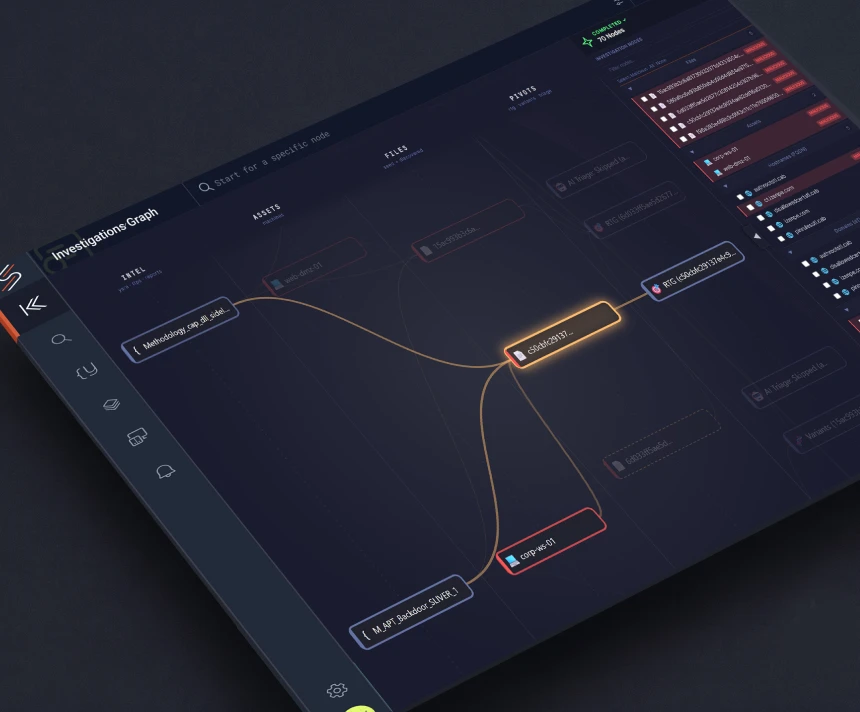
Backstory returns the full case: 
verdict, related files, affected hosts, attack stages, and remediation steps.

Rehunt 

the history

New intelligence runs across the files already collected and sends newly relevant matches back into the workflow.

Put the answer 

into action

Deliver reports, notifications, and remediation steps through SIEM, SOAR, case management, chat, webhook, and API workflows.

APIs and 


                        DOCUMENTATION

Public
API

Submit evidence, enrich existing data, and bring Stairwell results into custom workflows.

Webhooks

API

Push Stairwell event notifications to any platform that accepts webhooks.

Stairwell

Documentation

Access implementation 
guidance, integration instructions,
and API references.

Stairwell
GitHub

Use Stairwell-maintained repositories and resources to extend your integrations.