EVIDENCE COLLECTION

COLLECT THE FILES BEHIND
EVERY ALERT.

Alerts and logs describe the event. Stairwell preserves the executable behind it.
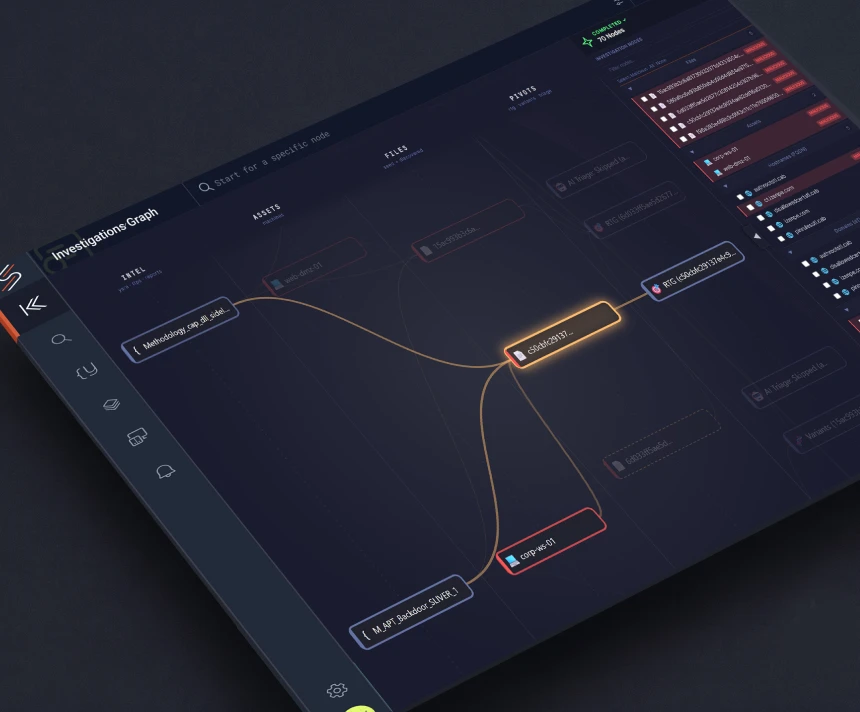
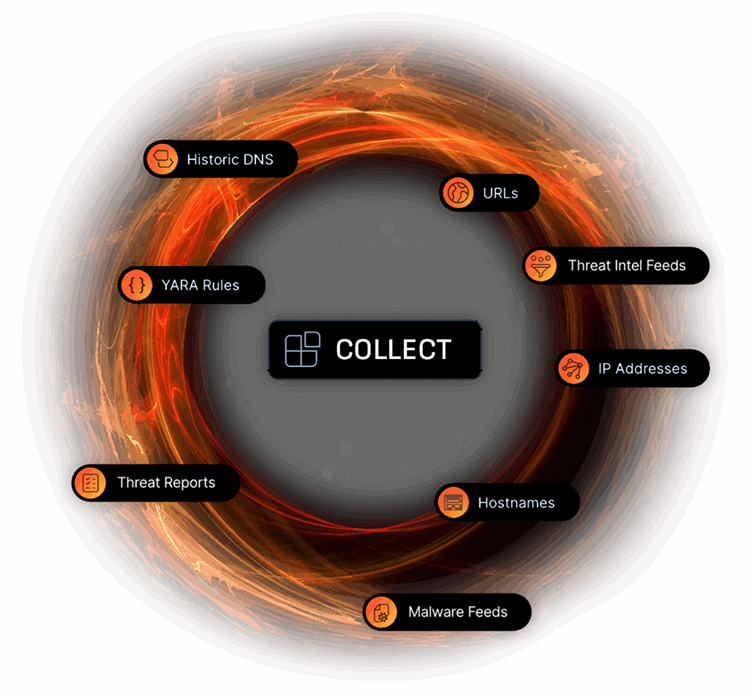
Collect executable files and scripts from your environment, together with the alerts, IOCs, YARA rules, DNS history, and threat reports that give them context. Every investigation starts with preserved file evidence, not only a record of the event.


How it works

Collect
the artifact

When an endpoint sees 
a new executable or an EDR raises an alert, Stairwell collects the file behind it. 


The artifact becomes evidence your team can search, analyze, and investigate.

Bring the context 

with it

Alerts, hashes, IOCs, 
YARA rules, DNS history, host details, and published research stay connected to the files they describe.

KEEP IT
PRIVATE

Enterprise files, 
private rules, and investigation results stay 
in your dedicated environment.

They are never added to a public repository.

Stay invisible 

to the attacker

Attackers can test 
against endpoint products and public analysis services. They cannot query Stairwell to learn what you collected, 
what you know, or what 
you are hunting.

COLLECTION

            CAPABILITIES

Every Endpoint Becomes
An Evidence Source

Continuously collect executables and 
scripts from enrolled Windows, macOS, 
and Linux endpoints. Each file keeps 
its provenance: where it appeared, when 
it arrived, and which hosts saw it.

Collect The File 

Behind The EDR Alert

An alert is more useful when the artifact is attached. Stairwell retrieves the suspicious file 
so Backstory can investigate the evidence independently.

Turn Reports 

Into Live Intelligence

Stairwell ingests indicators from public threat reports and checks them against the files already collected from your environment.


Add Active 

DNS History

Connect files to the domains and 
IP addresses they contacted over time, even after an attacker rotates infrastructure.

Operationalize 

Every YARA Rule

Use Stairwell-authored, community, 
or private YARA rules as always-on intelligence across every new and historical file.

FREQUENTLY ASKED QUESTIONS

Stairwell collects executable files and scripts from enrolled endpoints, plus the alerts and intelligence used to understand them.

A log records an event. The executable preserves the artifact. Keeping the file lets Stairwell investigate it now and rehunt it whenever intelligence changes.

No. Enterprise files, private rules, and investigation results remain in your dedicated environment.

The file is stored, analyzed, connected to relevant intelligence, and kept available for Backstory investigations and future rehunts.