CONTINUOUS REHUNT

REHUNT THE PAST. 

FIND WHAT CHANGED.

Stairwell keeps every executable forever and reruns new IOCs, YARA rules, 
threat reports, malware samples, and infrastructure intelligence across the full history.
A file cleared yesterday can become a detection tomorrow, without waiting for the attacker to return.

How it works

Keep 

the evidence

Every executable collected from 
your environment remains available for future hunts. The artifact does not expire when 
an alert closes 
or a retention window ends.

Add new 

intelligence

New malware samples, IOCs, YARA rules, threat reports, DNS history, and Stairwell research continuously add context.

Rehunt 

the full history

Each new signal runs across the files already in your dedicated environment and the Stairwell malware corpus.

Surface 

what changed

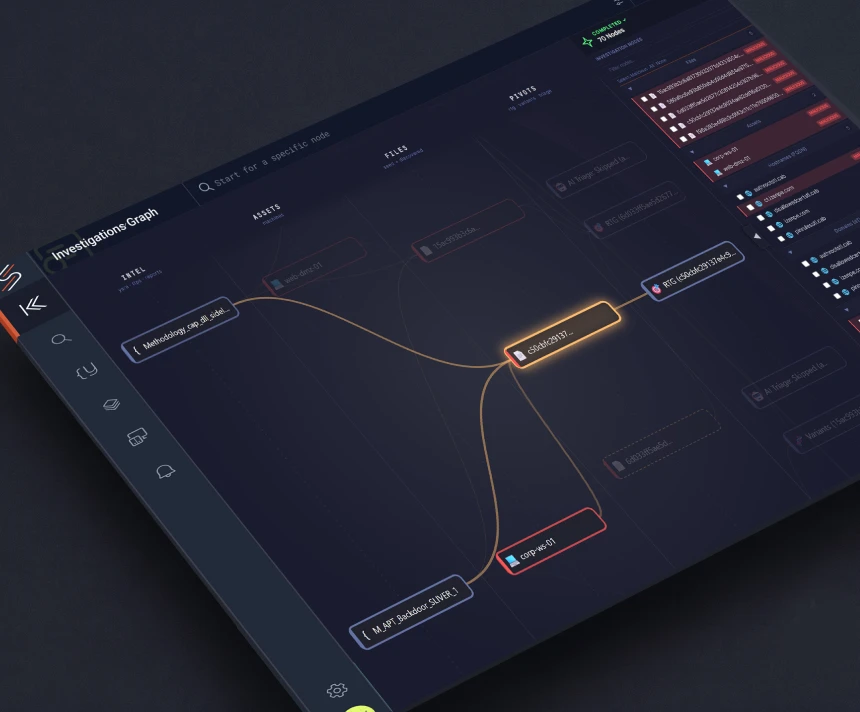
When a historical file now matches, Stairwell identifies the file, related variants, affected hosts, and the first point it appeared.

Send the match
to Backstory

A new detection becomes a complete investigation. Backstory scopes the blast radius, reconstructs the campaign timeline, and recommends what to do next.

REHUNT 


            CAPABILITIES

Automatic
Retrohunt

Turn every new IOC, rule, report, 
and malware sample into a hunt across 
the complete retained history.

YARA-X, 

Always On

Run Stairwell and private YARA rules over 
every past, present, and future file. A new rule 
can expose a threat that has been sitting quietly for months.

Check New Threat Reports 

Against Your History

When new campaign research is published, 
Stairwell checks the indicators against the preserved enterprise file history and shows whether the organization was affected.

Recursive 

Variant Discovery

A newly identified sample can surface 
the whole family, including variants that entered earlier under different names, 
hashes, or builds.

A Verdict 

That Can Change

Stairwell does not preserve yesterday’s 
answer as final. It updates the verdict as the evidence and intelligence change.

FREQUENTLY ASKED QUESTIONS

New IOCs, YARA rules, malware samples, threat reports, 
DNS and infrastructure context, and other intelligence can all trigger another search across historical files.

Yes. New intelligence is applied across the retained enterprise file history and relevant samples in the Stairwell malware corpus.

Yes. A verdict can change when new evidence connects the file to malware, infrastructure, a YARA rule, or a newly understood campaign.

No. Rehunting is continuous. Stairwell reruns intelligence across historical evidence without another manual search.

Because the future changes what the past means. Retaining the executable lets tomorrow’s intelligence search the evidence collected today.