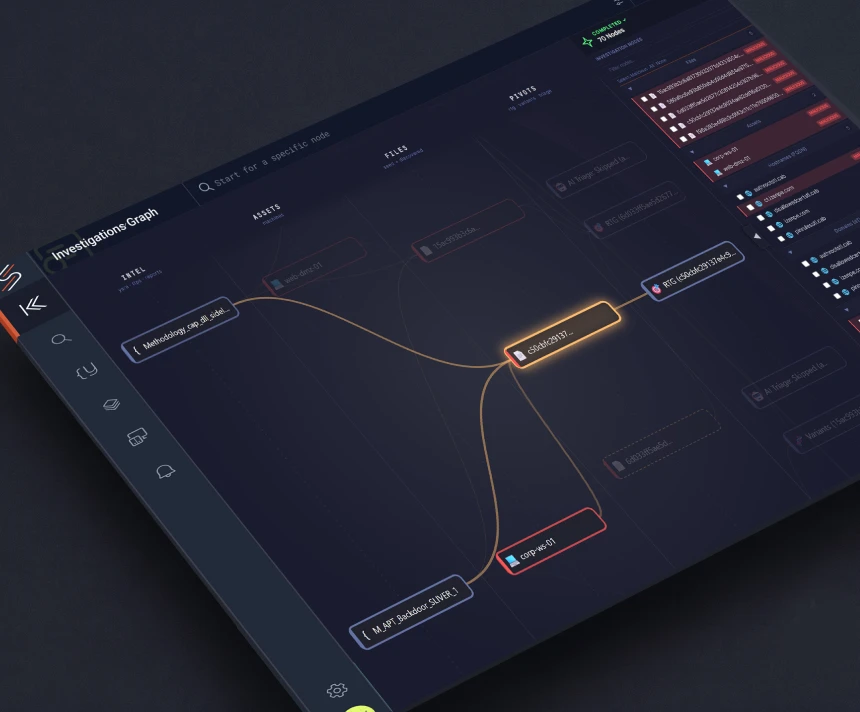
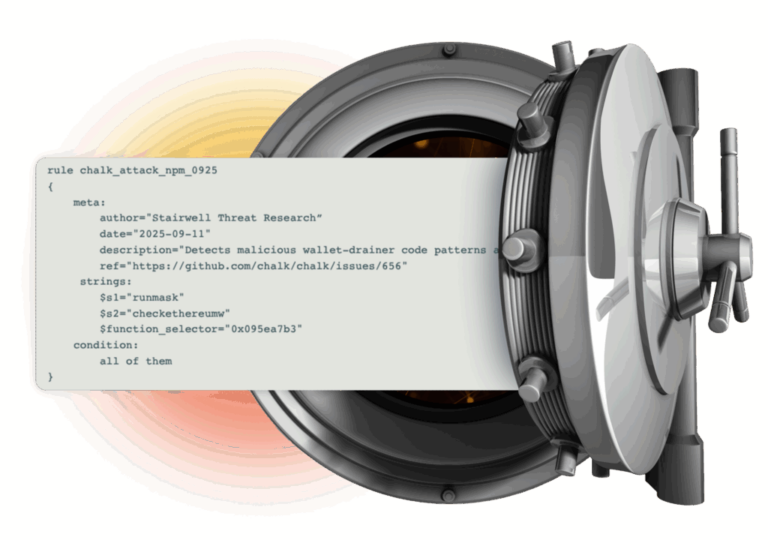
Security practitioners rely on a combination of structured intelligence resources and investigative tools during real investigations. Published threat reports provide context about known campaigns and actors. YARA rule libraries give hunters detection patterns to apply against file corpora. Malware analysis reports from trusted research teams document specific samples in depth. Case studies from peer organizations provide practical examples of how similar teams applied tools and techniques in real incident scenarios.
Security practitioners rely on a combination of structured intelligence resources and investigative tools during real investigations. Published threat reports provide context about known campaigns and actors. YARA rule libraries give hunters detection patterns to apply against file corpora. Malware analysis reports from trusted research teams document specific samples in depth. Case studies from peer organizations provide practical examples of how similar teams applied tools and techniques in real incident scenarios.
Security practitioners rely on a combination of structured intelligence resources and investigative tools during real investigations. Published threat reports provide context about known campaigns and actors. YARA rule libraries give hunters detection patterns to apply against file corpora. Malware analysis reports from trusted research teams document specific samples in depth. Case studies from peer organizations provide practical examples of how similar teams applied tools and techniques in real incident scenarios.

 Book a Demo